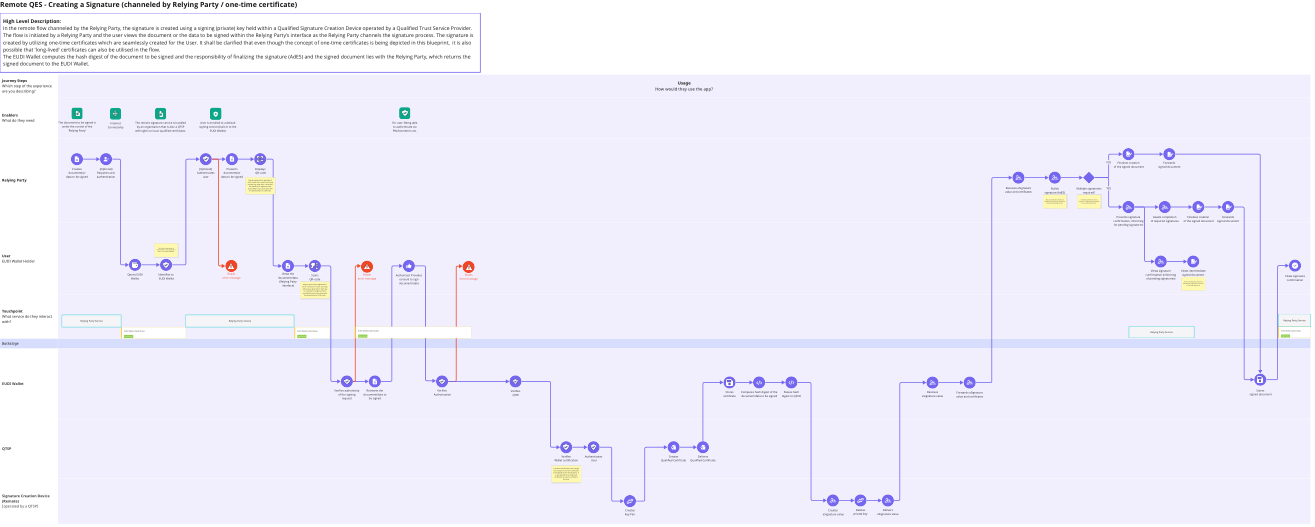
Remote QES - Creating a Signature (channeled by Relying Party / one-time certificate)
High Level Description:
In the remote flow channeled by the Relying Party, the signature is created using a signing (private) key held within a Qualified Signature Creation Device operated by a Qualified Trust Service Provider.
The flow is initiated by a Relying Party and the user views the document or the data to be signed within the Relying Party’s interface as the Relying Party channels the signature process. The signature is
created by utilizing one-time certificates which are seamlessly created for the User. It shall be clarified that even though the concept of one-time certificates is being depicted in this blueprint, it is also
possible that 'long-lived' certificates can also be utilised in the flow.
The EUDI Wallet computes the hash digest of the document to be signed and the responsibility of finalizing the signature (AdES) and the signed document lies with the Relying Party, which returns the
signed document to the EUDI Wallet.
Journey Steps
Usage
Which step of the experience
are you describing?
How would they use the app?
Enablers
What do they need
The document to be signed is Internet The remote signature service is handled User is enrolled to a default For user: Being able
under the control of the Connectivity by an organisation that is also a QTSP signing service (built-in to the to authenticate via
'Relying Party' with rights to issue qualified certificates. EUDI Wallet) PIN/biometrics etc.
NO Finalises creation Forwards
of the signed document signed document
Creates [Optional] [Optional] Presents Displays
document(s)/ Requests user Authenticates document(s)/ QR-code
data to be signed authentication user data to be signed
Relying Party May be optional/not applicable if
other interactions means are being
utilised (e.g. deep-link). It shall also
be examined in alignment with
accessibility issues associated with Receives eSignature Builds Multiple signatories YES
the presentation of a QR-code.
value and certificates signature (AdES) required?
May optionally fetch additional It shall be clarified that in this
elements to include, e.g. certificates, scenario, all signatories are signing
timestamps, signing time etc. the same document/form.
Presents signature Awaits completion Finalises creation Forwards
confirmation, informing of required signatures of the signed document signed document
for pending signatories
The 'Online Identification &
Authentication' flow described in
ARF v1.2.0' shall be followed.
User
EUDI Wallet Holder [Optional] Selects signing
service (QTSP) (note:
expected be indicated by Views signature Views intermediate
Opens EUDI Identifies to Reads Views the Reads Reads the Relying Party, e.g. in confirmation (informing signed document
Scans Authorizes/ Provides Views signature
Wallet EUDI Wallet error message document/data error message error message the QR-code) of pending signatories)
QR-code consent to sign confirmation
(Relying Party The non-finalised document that
May be optional/not applicable if
document/data includes their signature but not that
interface) other interactions means are being
of the other signatories
utilised (e.g. deep-link). It shall also
be examined in alignment with
accessibility issues associated with
the presentation of a QR-code.
Touchpoint
What service do they interact
Relying Party Service
with? Relying Party Service Relying Party Service
EUDI Wallet (Valid State) EUDI Wallet (Valid State) EUDI Wallet (Valid State) EUDI Wallet (Valid State)
Relying Party Service
Valid State Valid State Valid State Valid State
Backstage
EUDI Wallet
Verifies authenticity Retrieves the Verifies Verifies Stores
Stores Computes hash digest of the Passes hash Receives Forwards eSignature
of the signing document/data to Authorisation QTSP signed document
certificate document/data to be signed digest to QSCD eSignature value value and certificates
request be signed
QTSP
Verifies Authenticates Creates Delivers
Wallet certification User Qualified Certificate Qualified Certificate
It shall be clarified that even though
the concept of one-time certificates
is being depicted in this blueprint, it
is also possible that 'long-lived'
certificates can also be utilised in
the flow.
Signature Creation Device
(Remote)
(operated by a QTSP)
Creates Creates Deletes Delivers
Key Pair eSignature value private key eSignature value