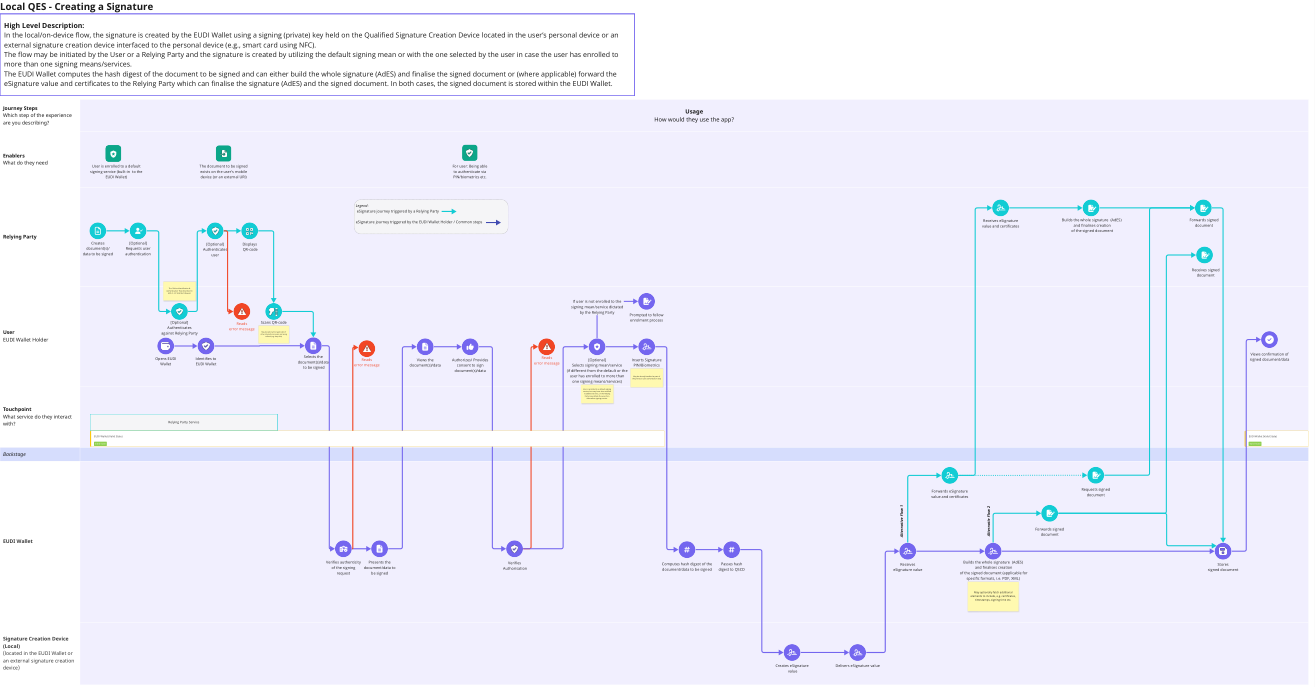
Local QES - Creating a Signature
High Level Description:
In the local/on-device flow, the signature is created by the EUDI Wallet using a signing (private) key held on the Qualified Signature Creation Device located in the user’s personal device or an
external signature creation device interfaced to the personal device (e.g., smart card using NFC).
The flow may be initiated by the User or a Relying Party and the signature is created by utilizing the default signing mean or with the one selected by the user in case the user has enrolled to
more than one signing means/services.
The EUDI Wallet computes the hash digest of the document to be signed and can either build the whole signature (AdES) and finalise the signed document or (where applicable) forward the
eSignature value and certificates to the Relying Party which can finalise the signature (AdES) and the signed document. In both cases, the signed document is stored within the EUDI Wallet.
Journey Steps
Usage
Which step of the experience
How would they use the app?
are you describing?
Enablers
What do they need
User is enrolled to a default The document to be signed For user: Being able
signing service (built-in to the exists on the user's mobile to authenticate via
EUDI Wallet) device (or an external URI) PIN/biometrics etc.
Legend:
eSignature journey triggered by a Relying Party
Receives eSignature Builds the whole signature (AdES) Forwards signed
eSignature journey triggered by the EUDI Wallet Holder / Common steps
value and certificates and finalises creation document
of the signed document
Relying Party
Creates [Optional] [Optional] Displays
document(s)/ Requests user Authenticates QR-code
data to be signed authentication user
Receives signed
document
The 'Online Identification &
Authentication' flow described in
ARF v1.2.0' shall be followed.
If user is not enrolled to the
signing mean/service dictated
by the Relying Party
Prompted to follow
enrolment process
[Optional] Reads Scans QR-code
Authenticates error message
User against Relying Party
May be optional/not applicable if
other interactions means are being
utilised (e.g. deep-link)
EUDI Wallet Holder
Views confirmation of
Selects the Reads Reads
Opens EUDI Authenticates
Identifies to Reads Views the Authorizes/ Provides [Optional] Inserts Signature signed document/data
document(s)/data error message
error message
Wallet inEUDI
EUDIWallet
Wallet error message document(s)/data consent to sign Selects signing mean/service PIN/Biometrics
to be signed
document(s)/data (if different from the default or the
user has enrolled to more than May be already handled as part of
the previous user authorisation step
one signing means/services)
User is enrolled to a default signing
service, but may have also enrolled
to additional ones, or the Relying
Party may dictate the use of an
alternative signing service.
Touchpoint
What service do they interact
Relying Party Service
with?
EUDI Wallet (Valid State) EUDI Wallet (Valid State)
Valid State Valid State
Backstage
Forwards eSignature Requests signed
value and certificates document
Alternative Flow 1
Alternatie Flow 2
Forwards signed
document
EUDI Wallet
Verifies authenticity Presents the Verifies Computes hash digest of the Passes hash Builds the whole signature (AdES)
Receives Stores
of the signing document/data to Authorisation document/data to be signed digest to QSCD and finalises creation
eSignature value signed document
request be signed of the signed document (applicable for
specific formats, i.e. PDF, XML)
May optionally fetch additional
elements to include, e.g. certificates,
timestamps, signing time etc.
Signature Creation Device
(Local)
(located in the EUDI Wallet or
an external signature creation
Creates eSignature Delivers eSignature value
device)
value